FeloxAC is a modular anti-cheat system for FiveM. It combines client-side detection modules with a server-side authority layer and a web dashboard, protecting your server against cheats, injectors, and exploited resources.
These docs cover everything you need to get FeloxAC running and integrated with your own resources:
Installation — license, resource placement, server.cfg, and the protection installer.
ACE Permissions — staff permissions from server.cfg: every admin-menu feature, bypass and commands as separate ACE objects.
Configuration — detections, punishment modes, and the Safe Events / Safe Scripts allowlists that stop false bans.
Client detection modules watch for cheat behaviour on each player and report to the server.
The server layer is authoritative — it confirms detections, applies the configured punishment (ban / kick / log), and records evidence (screenshots and gameplay clips) to your Discord webhooks.
The dashboard is the single source of truth for configuration. Settings are synced to your running server automatically and can be reloaded live with fac reload.
Requirements
Requirement
Value
FiveM artifact (server build)
14317 or newer
OneSync
Enabled (required)
fx_version
cerulean
Lua
lua54 'yes'
License
An active FeloxAC license (per server IP)
The in-game menu and all console commands use the fac prefix by default (for example fac install, fac reload, or the /fac menu). This prefix is configurable — see Configuration.
Installation
There are two ways in. The one-click installer does the whole setup for you, or you can follow the manual five-step route: get a license, add the resource, set your license.txt, update server.cfg, and run the protection installer.
Fast path — the one-click installer
feloxac-setup.exe automates steps 2 to 5 below: it extracts the resource, writes license.txt from your API token, configures server.cfg, and injects the third-party exports and guards. It runs locally on the machine that hosts the server. Get it from the Download page of your dashboard, together with the API token of the server you are installing on.
1
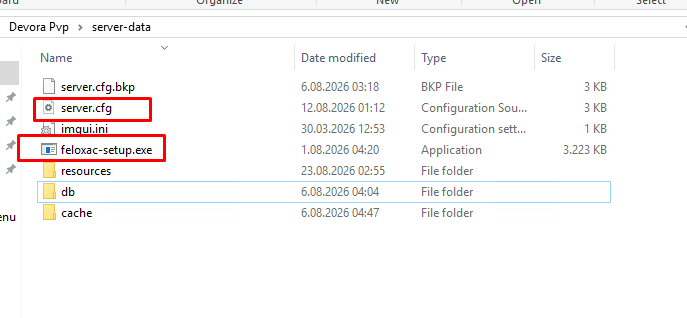
Put feloxac-setup.exe next to server.cfg
Drop the installer into your server folder — the same folder that holds server.cfg and resources/. Do not run it from your Downloads folder.
2
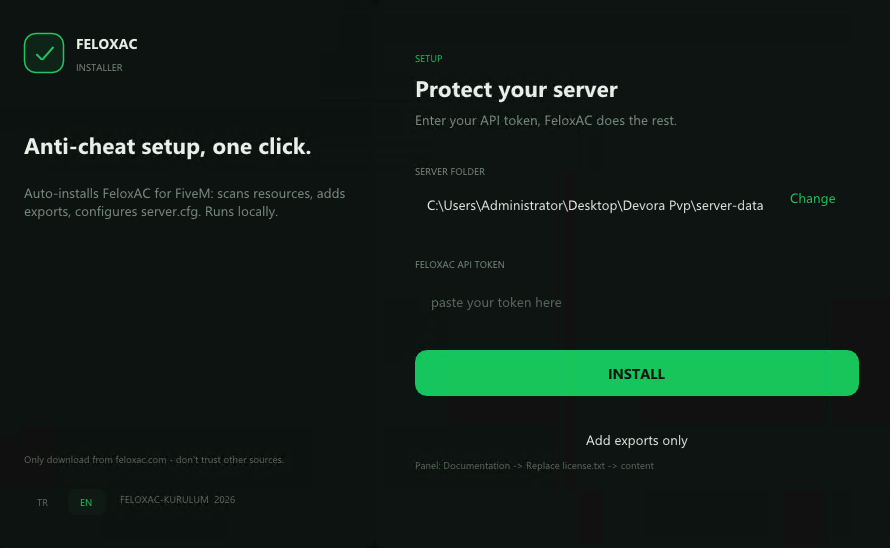
Open the program
Double-click feloxac-setup.exe. It detects the server folder on its own; if it shows the wrong path, use Change.
3
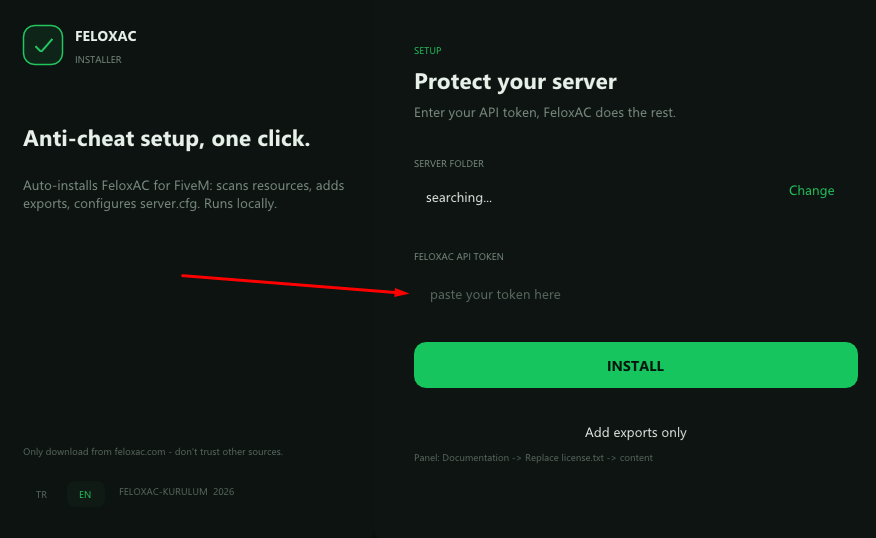
Paste your API token
Copy the token of your server from the dashboard and paste it into the FELOXAC API TOKEN field.
4
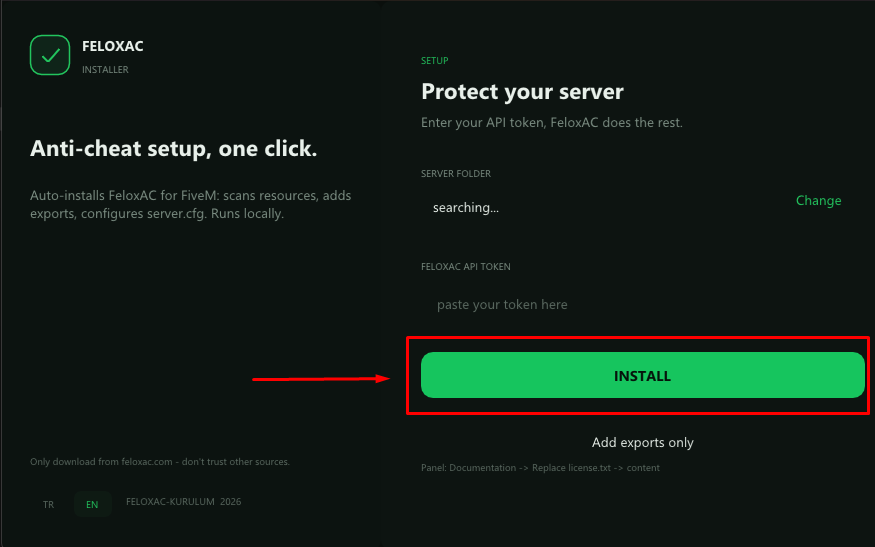
Press INSTALL
It extracts FeloxAC, writes license.txt, configures server.cfg and injects the exports. Restart your server when it finishes — you do not need to run fac install smart.
Already running FeloxAC and only need the third-party exports refreshed? Use Add exports only instead — it skips the package, the token and server.cfg. Because the file is unsigned, Windows SmartScreen may warn about an unknown publisher: choose More info → Run anyway.
Prefer to do it by hand? The manual route is below.
Your license is activated automatically after payment — there is no key to enter.
Open your dashboard and go to License. Under My Servers, enter your public server IP (the one in your connect address) and click Add server & get token. Your API token appears right there.
One license = one server. A second server needs its own license: buy it from Buy License and pick New server in the order step, then add the server on the License page. Renewing? Pick Extend: your server in the order step — the new period stacks on the remaining days. Got a key from staff or a reseller? Open Have a license key? on the License page and paste it.
Step 2 — Add the resource
Download the FeloxAC resource from your dashboard's Download page.
Extract it into your server's resources/ folder.
Make sure the folder is named FeloxAC.
The resource name must be FeloxAC — the server.cfg lines and all exports (exports['FeloxAC']) depend on it.
Step 3 — Configure license.txt
Open license.txt inside the FeloxAC folder and delete everything in it.
In your dashboard, go to Documentation → Replace license.txt.
Select your server, click Copy license.txt Content, and paste it into license.txt.
Save the file.
This file contains your API token. FeloxAC reads it at startup and validates it against feloxac.com for your server IP.
Add the ensure line at the very top of your ensure list, before every other resource:
ensure FeloxAC
Load order matters. FeloxAC must start first so it can inject its protection guards into your other resources.
Staff permissions (ACE) — optional
Staff permissions (admin menu, bypass, commands) are also given from server.cfg. They have their own section: ACE Permissions.
Step 5 — Run the protection installer
Copying the resource is not enough — you must run the installer once so FeloxAC protects your other scripts.
Start your server.
Open the Live Console (txAdmin or the server console) and run:
fac install smart
Wait for the installation to finish.
Restart your server. FeloxAC is now active.
What fac install smart does
It scans every resource and installs FeloxAC protection only into scripts that use network events. Resources with no network events (vehicles, peds, maps, libraries) are skipped automatically, so the install stays fast and clean.
Other install modes
Command
Description
fac install smart
Recommended. Only protects resources that use network events.
fac install / fac install all
Protects every resource.
fac install optimize
Protects only entity-spawn and inventory guards (for very heavy servers).
Verify the installation
Run status (or check txAdmin) — FeloxAC should appear in the resource list.
The server console prints FeloxAC's startup and license validation result.
Connecting players are logged (join/leave) if connection logging is enabled.
Troubleshooting
License is invalid / players get kicked
Confirm license.txt contains the exact token from your dashboard.
Confirm your server's public IP matches the IP registered for the license.
Make sure the server can reach https://feloxac.com (check firewall / hosts file). FeloxAC is fail-closed — if it cannot validate the license it stops and kicks players by design.
fac command not found
Confirm the FeloxAC resource is running (status).
The command prefix is fac, not feloxac. If you changed CommandPrefix in config, use your custom prefix.
Detections not firing after install
Confirm ensure FeloxAC is at the top of your ensure lines.
Confirm OneSync is on (set onesync on).
Confirm your server build is 14317+.
Re-run fac install smart and restart.
ACE Permissions
Staff permissions can be granted straight from server.cfg with FiveM's ACE system — the same add_ace / add_principal lines you already use for txAdmin and your other resources. Every part of the in-game /fac admin menu has its own permission, so a moderator can get bans and kicks without troll options or vehicle spawn.
ACE and the web panel work side by side. ACE lines are server.cfg trust: whatever you allow here cannot be narrowed from the panel. People without ACE lines get exactly the permissions you tick for them on the dashboard's Admins page. txAdmin admins additionally receive a limited bypass automatically.
All permissions
Objects are hierarchical, exactly like FiveM's own command / command.kick: allowing FeloxAC.AdminMenu allows everything under it, and a more specific deny beats a broader allow.
AdminMenu — the in-game /fac menu
ACE object
What it unlocks
FeloxAC.AdminMenu
The whole menu — every row below, plus anything added in future versions.
FeloxAC.AdminMenu.Players
Players tab: the online player list with identifiers, trust score and badges.
FeloxAC.AdminMenu.Tools
Admin tools and the Self tab: noclip, freecam, ESP, teleport to / bring / freeze a player, inspect and delete entities. Required for Troll and CarSpawn below.
FeloxAC.AdminMenu.CarSpawn
Vehicle spawn from the Self tab (needs Tools).
FeloxAC.AdminMenu.Troll
Troll options: ped change, super jump, vehicle jump (needs Tools).
FeloxAC.AdminMenu.Monitor
Live screen: watch a player's screen in real time.
FeloxAC.AdminMenu.Bans
Ban list, ban a player, unban, unban all.
FeloxAC.AdminMenu.Kicks
Kick a player.
FeloxAC.AdminMenu.Entities
Clear world: delete every spawned vehicle / ped / object at once.
FeloxAC.AdminMenu.Messages
Staff chat and direct messages to players.
FeloxAC.AdminMenu.Announcements
Server-wide announcements (shown to every player).
FeloxAC.AdminMenu.Lookup
Discord lookup of a player.
FeloxAC.AdminMenu.Logbook
Logs tab: detection history on this server.
FeloxAC.AdminMenu.AdminLogs
Admin Logs tab: who did what from the panel and the menu.
FeloxAC.AdminMenu.Settings
View and change the anti-cheat configuration from the menu.
FeloxAC.AdminMenu.Admins
Manage admins, moderators, staff and the bypass list.
Bypass
ACE object
What it does
FeloxAC.Bypass
Full detection bypass. The player is never banned, kicked or warned by FeloxAC. Give it only to people you trust completely — there is no partial version on purpose.
Commands
ACE object
What it does
FeloxAC.Commands
Console and chat commands such as clearing entities or unbanning everyone (fac ...).
Shortcut — allow a whole group
You don't have to list every object. Allow the category and everyone in that group gets all of it:
add_ace group.admin FeloxAC.AdminMenu allow
Take one feature back from the same group with a more specific deny:
# FELOXAC PERMISSIONS in server.cfg
# add_ace [principal] [object] [allow|deny]      -> grants (or denies) an object to a group / identifier
# add_principal [child_principal] [parent_principal] -> puts an identifier into a group
# Any FiveM identifier works: discord, steam, license, fivem, ip, xbl, live.
# Find someone's identifiers in txAdmin > Players, or on the FeloxAC dashboard > Players.

# SUPER ADMINS
add_principal identifier.discord:123456789012345678 group.superadmin

# ADMINS
add_principal identifier.discord:234567890123456789 group.admin
add_principal identifier.license:1a21a2380bca020822ad301eb4e579e00a7063f3 group.admin

# MODERATORS
add_principal identifier.discord:345678901234567890 group.mod

# PERMISSIONS GIVEN TO SUPER ADMINS
add_ace group.superadmin FeloxAC.AdminMenu allow
add_ace group.superadmin FeloxAC.Commands allow
add_ace group.superadmin FeloxAC.Bypass allow

# PERMISSIONS GIVEN TO ADMINS
add_ace group.admin FeloxAC.AdminMenu allow
add_ace group.admin FeloxAC.AdminMenu.Admins deny

# PERMISSIONS GIVEN TO MODERATORS
add_ace group.mod FeloxAC.AdminMenu.Players allow
add_ace group.mod FeloxAC.AdminMenu.Tools allow
add_ace group.mod FeloxAC.AdminMenu.Monitor allow
add_ace group.mod FeloxAC.AdminMenu.Bans allow
add_ace group.mod FeloxAC.AdminMenu.Kicks allow
add_ace group.mod FeloxAC.AdminMenu.Messages allow
add_ace group.mod FeloxAC.AdminMenu.Lookup allow
add_ace group.mod FeloxAC.AdminMenu.Logbook allow
Write the object names exactly as listed (FeloxAC.AdminMenu.CarSpawn). After editing permissions run refresh in the server console and let the person reconnect, or restart the server.
Which one should I use — ACE or the panel?
Panel (Admins page) — per person, changeable at any time without touching files, synced live to the server. Best for day-to-day staff management.
ACE (server.cfg) — per group, lives with the rest of your server permissions, survives panel changes. Best for owners and for servers that manage every permission in server.cfg.
Both can be used at once. A person who has both gets the union of the two.
Configuration
FeloxAC is configured from your dashboard. Everything is done through the panel — toggles, dropdowns, and list ("chip") inputs — so you never edit raw config files by hand.
Changes are synced to your running server automatically. To apply them immediately, run:
fac reload
Your server keeps the last synced configuration in memory as a fallback. If feloxac.com is unreachable at startup, FeloxAC retries and, if it still cannot validate, stops by design (fail-closed).
How the panel works
Toggles turn a detection on or off.
Dropdowns choose the action for a detection (Ban / Kick / Log).
Lists (chips) hold multiple values — such as Safe Events, Safe Scripts, and the white/black lists. To add an item, type it into the "New item, press enter to add…" box and press Enter. To remove one, click the ✕ on its chip.
Sections at a glance
Section
Purpose
Settings
Server-wide options: bans, webhooks, logging, command prefix, and script allowlists.
Main
Movement & general client cheats (no-clip, teleport, speed, godmode, injection, event spoofing).
Weapons
Combat & weapon detections (aimbot, damage, ammo, blacklists).
Entities
Vehicle / ped / object spawning and manipulation.
Explosions
Explosion & particle detections.
Punishments
Per-detection action: Ban, Kick, or Log.
Punishment modes (Ban / Kick / Log)
Mode
Behaviour
Ban
Permanently bans the player (until unbanned from the dashboard).
Kick
Disconnects the player; they can rejoin.
Log
No punishment. Records the detection with video / screenshot evidence only.
Log mode is your tuning tool. Set a detection to Log while you test it — you still get full evidence and telemetry, but nobody is punished. Once you've confirmed it's accurate, switch it to Kick or Ban.
Safe Events — stop false bans from events
Where: Settings → Safe Events list.
Some legitimate scripts give a weapon or teleport a player through a network event. If that event trips a detection, honest players get false-banned. Add the offending event name to Safe Events and FeloxAC will skip weapon-give / teleport detection for it.
How to add one: type the event name into the Safe Events box and press Enter — for example job:teleportToWork or police:warpToStation. It appears as a chip in the list.
How to find the event name:
Check the detection log / Discord evidence — the triggering event is included in the ban details.
Or check the script's source for the TriggerServerEvent / TriggerClientEvent name it fires when teleporting or giving the weapon.
Only add events you trust. Safe Events disables detection for that event, so any player who can trigger it bypasses that check.
Safe Scripts — trust a whole resource
Where: Settings → Safe Scripts list.
Where Safe Events whitelists a single event, Safe Scripts trusts an entire resource. Add a resource here when it legitimately teleports players or gives weapons and you don't want to whitelist each event individually — for example job systems, rental systems, admin menus, or weapon shops.
How to add one: type the resource name into the Safe Scripts box and press Enter (for example my-rental-system). Matching is case-insensitive.
The bundled fac-weapons helper only works once you add fac-weapons to your Safe Scripts list.
Blacklisted weapons are always rejected, even for a Safe Script. Safe Scripts relax the give-weapon / teleport checks, but they never override the weapon blacklist.
Ignored Scripts — fully exclude a resource
Where: Settings → Ignored Scripts list.
Ignored Scripts disables all FeloxAC checks for a resource — weapons, entities, events, everything. Use it only for a fully trusted resource that is otherwise incompatible with the anti-cheat.
Use with caution. An ignored resource is a blind spot: if a cheater can execute code inside it, FeloxAC will not see it. Prefer Safe Events or Safe Scripts whenever possible.
Which one should I use?
Situation
Use
One event from a script causes false bans
Safe Events
A whole resource legitimately teleports / gives weapons
Safe Scripts
A resource is incompatible and must be fully excluded
Ignored Scripts
White lists & black lists
Entities and weapons use the same chip inputs. Type a model name or hash (or weapon name) and press Enter.
List
What it does
White Listed Peds
Ped models that are always allowed (stops repeated ped false bans).
White Listed Objects
Object models that are always allowed.
White Listed Vehicles
Vehicle models that are always allowed.
Weapons Black List
Weapons players may never have (e.g. weapon_rpg, weapon_minigun).
Seeing repeated false bans from the same ped, object, or vehicle? Whitelisting that model is the fix — see False Bans.
Key detection toggles
Main
Toggle
Default
Purpose
Anti No-Clip
On
Detect no-clip.
Anti Teleport
Off
Detect teleport (position jumps).
Teleport Max Distance
200
Distance (metres) that counts as a teleport.
Anti Speed Hack
On
Detect speed hacks.
Anti Super Jump
On
Detect super jump.
Anti Resource Injection
On
Detect malicious resource injection.
Anti Resource Stop
On
Prevent stopping the FeloxAC resource.
Anti Trigger Server/Client Event
On
Block spoofed events.
Client Revive Event
—
Your custom revive event name (avoids revive false bans).
Weapons
Toggle
Default
Purpose
Anti Aim Bot / Silent Aim
On
Detect aimbot & silent aim.
Anti Weapon Damages Modifier
On
Detect damage multipliers.
Max Damage Multiplier
2
Max allowed damage multiplier.
Anti Give Weapons
On
Detect illegitimate weapon gives.
Weapons Black List
Off / list
Weapons players may never have.
Entities
Toggle
Default
Purpose
Anti Spawn Isolated Vehicles
On
Detect vehicles spawned without owner context.
Same Owner Vehicle Spawn Limit
3
Max vehicles one player may own.
Vehicles Limit In 5 Seconds
7
Vehicle spawn rate limit.
Anti Request Control
On
Detect entity control hijacking.
Anti Attach Vehicles
On
Detect illegal vehicle attaching.
For scripts that legitimately teleport or give weapons, prefer Safe Events / Safe Scripts over disabling a whole detection. Turning a detection off removes protection for every player.
False Bans
Almost every false ban comes from an object, a vehicle, or a ped. In the vast majority of cases it is not the detection that is wrong — it is one of two things:
The anti-cheat was not fully installed (the protection installer was never run), or
Your server basics are not set up correctly (OneSync / license), or
A legitimate resource keeps spawning the same entity, which just needs to be whitelisted.
Work top to bottom: fix the setup first, and only whitelist a specific model if the same ped / object / vehicle keeps triggering the ban.
Step 1 — Check your setup first
Most false bans disappear the moment the basics are correct:
OneSync is ON — set onesync on
OneSync population is OFF — set onesync_population false (this one is the most commonly forgotten)
You have a paid FiveM (Keymaster) account — free / unlicensed setups cause detection problems
You ran the installer — fac install smart, then restarted the server
If any of these is missing, fix it and test again before whitelisting anything.
Ban reason → what to fix
Look up the reason shown on the ban or on the detection log, and apply the fix next to it.
Illegal Object Spawn Detected
A resource spawned an object the anti-cheat does not recognise. If the object is legitimate and it is always the same one, whitelist it:
Config → Entities → White Listed Objects — type the model name or hash, press Enter.
Make sure Enable Objects White List is ON, otherwise the list is ignored.
Run fac reload (or restart) to apply.
Exceeded Object / Vehicle / Ped Spawn Rate
This is a rate limit, not a model problem: a script spawned more entities within 5 seconds than the limit allows. In Config → Entities you can raise the limit or turn the limiter off:
Raise the limit first. Only turn a limiter off when a legitimate resource genuinely needs bulk spawning (map loaders, garages, event scripts).
Illegal Vehicle Spawn Detected
This almost always means the resource that spawns the vehicle does not have the FeloxAC include installed. Without it the spawn arrives unsigned, and the anti-cheat cannot tell it apart from an injected one.
Find which resource spawns the vehicle, and make sure the include is installed in that resource.
Run fac install smart and restart the server — it injects the include into eligible resources.
If it still fires after the include is confirmed installed, contact us — do not whitelist your way around this one. A missing include is a real protection gap, and whitelisting hides it instead of fixing it.
Resource Injection Detected
Read the detail line of the detection — it tells you which of the two fixes you need:
The detail names an event → add that event to Config → Main → Safe Events.
The detail shows a file path like @@Script/test.lua → add it to Config → Main → Anti Resource Injection Safe List, but without the @@: type Script/test.lua.
Entries match as a substring of the callsite path, so you choose how wide the exemption is:
my-resource/client/cl-garage.lua — exempts that one file (preferred).
my-resource — exempts every file in that resource (much wider; use only if you have to).
Always start with the narrowest entry that stops the false ban. This exemption only suppresses the callsite mismatch — the rest of the injection checks stay active either way.
Ped false bans
If players are getting false-banned from a ped, it is almost always one of these:
OneSync is not on
No paid FiveM Keymaster account
onesync_population is not set to false (the forgotten command)
fac install smart was not run
Fix those first. If the ban always comes from the same ped, that ped is legitimate — add its model to the White Listed Peds list.
Object false bans
If the anti-cheat keeps banning from objects in general, fac install smart was most likely not run, so the protection was never installed. Run it and restart.
If the ban is always from the same object, that object is legitimate — add it to the White Listed Objects list.
Vehicle false bans
Make sure fac install smart has been run and the server restarted.
If a specific, legitimate vehicle is repeatedly flagged, add it to the White Listed Vehicles list.
How to whitelist a model
Whitelisting is done from the dashboard, using the chip inputs:
White Listed Peds — for peds
White Listed Objects — for objects
White Listed Vehicles — for vehicles
Type the model (name or hash) into the "New item, press enter to add…" box and press Enter. Then run fac reload (or restart) to apply.
Only whitelist a model when you are sure it is legitimate. A whitelisted model is no longer checked, so don't whitelist something a cheater could abuse — fix the setup instead whenever possible.
When it's a script, not an entity
If the false ban is caused by a resource that teleports players or gives weapons (not by a spawned entity), use Safe Events or Safe Scripts instead — see Configuration.
Developer API (Exports)
FeloxAC exposes exports so your resources can ban/kick players, read player state, and tell the anti-cheat when an action is legitimate (admin teleports, heals, weapon gives, and so on).
All exports are called on the FeloxAC resource:
exports['FeloxAC']:exportName(args)
Call server exports from server scripts and client exports from client scripts. For the ban export, see the dedicated Ban Export page.
Server exports
Moderation
Export
Signature
Description
banPlayer
(source, reason, details?, duration?)
Ban a player. duration in seconds, -1 = permanent.
kickPlayer
(source, reason, details?, duration?)
Kick a player.
unbanPlayer
(banId, reason, from)
Unban a single ban by its ban ID.
unbanAllPlayers
(from)
Unban everyone.
getBanInfo
(banId) → found, banData
Look up a ban by ID.
screenshot
(source, webhook)
Screenshot a player and upload to a Discord webhook.
captureLastSeconds
(source, webhook)
Upload the player's last ~10s of gameplay to a webhook.
-- Ban a player for 1 hour (3600 seconds)
exports['FeloxAC']:banPlayer(source, 'Aimbot', { by = 'Admin' }, 3600)

-- Unban by id
exports['FeloxAC']:unbanPlayer('BAN-ID-HERE', 'Appeal accepted', 'HeadAdmin')

-- Kick instead of banning
exports['FeloxAC']:kickPlayer(source, 'AFK too long', { by = 'Admin' })

-- Look up a ban, then lift every ban on the server
local found, banData = exports['FeloxAC']:getBanInfo('BAN-ID-HERE')
if found then print(banData.reason) end
exports['FeloxAC']:unbanAllPlayers('HeadAdmin')

-- Evidence straight to a Discord webhook
exports['FeloxAC']:screenshot(source, 'https://discord.com/api/webhooks/...')
exports['FeloxAC']:captureLastSeconds(source, 'https://discord.com/api/webhooks/...')
Player state
Export
Signature
Description
getPlayerIdentifiers
(netId) → table
All identifiers (license, discord, ip…). Respects BanIpAddress.
getPlayerTokens
(netId) → table
The player's hardware/session tokens.
getThreatScore
(playerId) → number|nil
The player's cumulative threat score.
getPlayTime
(playerId) → number|nil
The player's play time this session.
hasBypass
(playerId) → boolean
Whether the player has anti-cheat bypass permission.
-- Everything FeloxAC knows about a connected player
local ids    = exports['FeloxAC']:getPlayerIdentifiers(source)
local tokens = exports['FeloxAC']:getPlayerTokens(source)
local score  = exports['FeloxAC']:getThreatScore(source)
local played = exports['FeloxAC']:getPlayTime(source)

print(ids.license, ids.discord, #tokens, score, played)

-- Skip your own admin checks for a player FeloxAC already exempts
if exports['FeloxAC']:hasBypass(source) then return end
Configuration
Export
Signature
Description
ReloadConfiguration
() → boolean
Reload configuration without a restart (same as fac reload).
-- Apply config edits without restarting the resource (same as: fac reload)
if exports['FeloxAC']:ReloadConfiguration() then
    print('FeloxAC config reloaded')
end
Legitimate-action markers (server)
These tell FeloxAC that an action performed by your script is intentional, so a detection does not fire. They are not security bypasses — they scope an allowance to a specific action.
Export
Signature
Description
markExternalTeleport
(sourceId, fallbackSource?)
Mark an upcoming teleport of this player as legitimate.
markExternalHeal
(sourceId, fallbackSource?)
Mark a heal of this player as legitimate.
registerLegalPedModel
(playerId, model)
Allow a ped-model change for this player.
registerLegalSpeedModifier
(playerId)
Allow a movement-speed change for this player.
registerLegalWeapon
(playerId, weaponHash)
Mark a weapon as legitimately owned (inventory integration).
unregisterLegalWeapon / clearLegalWeapons
(playerId, weaponHash?)
Remove one / all legal-weapon registrations.
registerLegalSuperJump
(playerId, durationMs)
Allow super jump for a duration (ms).
CreateEntity
(modelHash) → entity
Create a server entity pre-approved by the anti-cheat.
MarkServerEntity
(entity, modelHash)
Mark an existing server entity as legitimate.
unregisterLegalSuperJump
(playerId)
Remove a super-jump allowance before it expires.
registerLegalNoclip
(playerId, durationMs?) → boolean
Tell FeloxAC that this player is using your admin menu's noclip. Opens a short exemption window (default 30000 ms, capped at 600000). Call it again to renew while noclip stays on.
unregisterLegalNoclip
(playerId) → boolean
Close the noclip window immediately (call it when noclip is turned off).
markVoiceOverrideActive
(sourceId, active, fallbackSource?) → boolean
Mark that your script is legitimately overriding voice range/channel for this player (radio, megaphone). Call with true when the override starts and false when it ends.
-- Admin teleports a player without a false ban
exports['FeloxAC']:markExternalTeleport(target)
SetEntityCoords(GetPlayerPed(target), x, y, z)

-- Heal a player from a server script
exports['FeloxAC']:markExternalHeal(target)

-- A job script hands out a weapon: register it, or the possession sweep bans
local weapon = GetHashKey('weapon_pistol')
exports['FeloxAC']:registerLegalWeapon(target, weapon)

-- ...and drop the registration when you take the weapon back
exports['FeloxAC']:unregisterLegalWeapon(target, weapon)
exports['FeloxAC']:clearLegalWeapons(target)   -- or drop every one at once

-- Ped model change (skin menu, job outfit). Pass nil to accept the current model.
exports['FeloxAC']:registerLegalPedModel(target, 'a_m_y_business_01')

-- Parkour / minigame super jump. durationMs is in MILLISECONDS.
exports['FeloxAC']:registerLegalSuperJump(target, 30000)
exports['FeloxAC']:unregisterLegalSuperJump(target)   -- end it early

-- Noclip from your own admin menu. Call it SERVER-side, after your own admin check.
-- durationMs is in MILLISECONDS (default 30000, capped at 600000 = 10 min).
exports['FeloxAC']:registerLegalNoclip(target)          -- when noclip is enabled
exports['FeloxAC']:registerLegalNoclip(target, 60000)   -- ...or ask for a longer window
exports['FeloxAC']:unregisterLegalNoclip(target)        -- when noclip is disabled

-- Megaphone / radio. Sticky: pair every true with a false.
exports['FeloxAC']:markVoiceOverrideActive(target, true)
exports['FeloxAC']:markVoiceOverrideActive(target, false)

-- Server-side spawn: create it pre-approved, or mark a handle you already hold
local veh = exports['FeloxAC']:CreateEntity(GetHashKey('adder'))
exports['FeloxAC']:MarkServerEntity(veh, GetHashKey('adder'))
registerLegalNoclip covers the noclip itself plus the side effects of flying: teleport, speed, vehicle warp, camera and invisibility. Everything else still bans while the window is open — weapons/aimbot, god mode, blacklisted spawns, overlays, and any tampering with FeloxAC itself. Manual bans and kicks from the /fac menu and the dashboard keep working too. It needs no server.cfg entry; set feloxac_script_noclip 0 is an emergency kill switch that is on by default.
This export says "this player is using noclip right now" — it does not say "this player is an admin". Run your own permission check before you grant noclip, and call the export from the server. If you hook it to a client event, any cheater can trigger that event and open the window themselves. Renew it roughly every 10 seconds while noclip is on; if renewals stop, the window expires on its own.
Bypass & diagnostics (server)
Export
Signature
Description
toggleBypass
(playerId, toggle)
Turn full detection bypass on/off for a player (events, freeroam zones).
tempBypass
(playerId, duration)
Same, but expires automatically after duration.
IsEventProtected
(eventName) → boolean
Whether an event name is on FeloxAC's protected-event list.
-- Freeroam / event zone: lift detections, then always put them back
exports['FeloxAC']:toggleBypass(target, true)
-- ...
exports['FeloxAC']:toggleBypass(target, false)

-- Safer: a self-expiring window. duration is in SECONDS (capped at 43200 = 12 h).
exports['FeloxAC']:tempBypass(target, 60)

-- Is this event name already on FeloxAC's protected list?
if exports['FeloxAC']:IsEventProtected('myresource:giveMoney') then
    print('already protected')
end
toggleBypass and tempBypass work out of the box — you do not need to add anything to server.cfg for them. feloxac_runtime_bypass is an emergency kill switch that is on by default, not a setup step: only set set feloxac_runtime_bypass 0 if you ever want to disable all runtime bypass server-wide, and set feloxac_runtime_bypass 1 (or just remove the line) to turn it back on.
A bypassed player is exempt from every detection while the window is open — scope it tightly, prefer tempBypass with a short duration, and always pair toggleBypass(id, true) with a false call when the reason ends.
Client exports
Client exports are markers: they tell FeloxAC that what your script is about to do is legitimate. Apart from banPlayer, kickPlayer, screenshot and captureLastSeconds, they do not perform the action for you. The pattern is always the same — mark first, then call the game native:
exports['FeloxAC']:markExternalTeleport()
SetEntityCoords(PlayerPedId(), x, y, z, false, false, false, false)
The weapon, damage and immortality markers read GetInvokingResource() and ignore calls that have none, so they cannot be driven from an executor. Their allowances are time-boxed too — a marker opens a short window, it never switches a detection off permanently.
Declare the ped model you are about to apply — name or hash. Returns true when the call came from a resource. Repeat refreshes are rate-limited to one per 60 s.
exports['FeloxAC']:displayInputBox()
Call it right before DisplayOnscreenKeyboard so the input-box detection does not fire.
Allow targeting / lock-on ped flags for durationMs — default 5000, capped at 60000. Returns false when there is no invoking resource. For cuff, carry, cutscene and safezone scripts.
exports['FeloxAC']:MarkVehicleRepair()
Call it immediately before repairing a vehicle (mechanic scripts), then call SetVehicleFixed yourself.
-- Every marker below follows the same shape: mark first, then call the native.
exports['FeloxAC']:hasTeleported()          -- same marker as markExternalTeleport()
SetEntityCoords(PlayerPedId(), x, y, z, false, false, false, false)

exports['FeloxAC']:healthRefilled()         -- same marker as markExternalHeal()
SetEntityHealth(PlayerPedId(), 200)

exports['FeloxAC']:playerRevived()
exports['FeloxAC']:resettedStamina()        -- opens a ~10 s window
exports['FeloxAC']:hasAddedAmmo()           -- opens a ~5 s window

-- Declare the ped model before you apply it (name or hash). Returns true when the
-- call came from a resource; repeat refreshes are capped at one per 60 s.
exports['FeloxAC']:hasChangedPedModel('a_m_y_business_01')
SetPlayerModel(PlayerId(), GetHashKey('a_m_y_business_01'))

-- Right before an on-screen keyboard
exports['FeloxAC']:displayInputBox()
DisplayOnscreenKeyboard(1, 'FMMC_KEY_TIP8', '', '', '', '', '', 30)

-- Cuff / carry / cutscene / safezone. durationMs defaults to 5000, capped at 60000.
exports['FeloxAC']:allowImmortalityFlags(10000)

-- Mechanic script repairing a vehicle
exports['FeloxAC']:MarkVehicleRepair()
SetVehicleFixed(veh)
Godmode / player state (client)
These are state switches, not one-shot markers: whatever you turn on, you have to turn off again.
Call
What it does
exports['FeloxAC']:proofsEnabled(toggle)
Turn proof-of-life checks on/off for legitimate godmode scripts.
exports['FeloxAC']:canBeDamaged(toggle)
Declare whether the player can currently take damage. Pass false when you make them invulnerable, true when you release it.
exports['FeloxAC']:isInvincible(toggle)
Declare a legitimate invincibility window. Pair every true with a false.
exports['FeloxAC']:isVisible(toggle)
Declare visibility. Pass false before you hide the ped, true when it is visible again.
exports['FeloxAC']:canRagdoll(toggle)
Declare that ragdoll is legitimately disabled / enabled.
exports['FeloxAC']:setSpectatorMode(toggle)
Turn legitimate spectate on/off.
-- admin goes invisible, then comes back
exports['FeloxAC']:isVisible(false)
SetEntityVisible(PlayerPedId(), false, false)
-- ...
exports['FeloxAC']:isVisible(true)
SetEntityVisible(PlayerPedId(), true, false)

-- The rest of the switches follow the same on/off discipline
exports['FeloxAC']:proofsEnabled(false)
exports['FeloxAC']:canBeDamaged(false)
exports['FeloxAC']:isInvincible(true)
SetEntityInvincible(PlayerPedId(), true)
-- ...release everything you turned on
SetEntityInvincible(PlayerPedId(), false)
exports['FeloxAC']:isInvincible(false)
exports['FeloxAC']:canBeDamaged(true)
exports['FeloxAC']:proofsEnabled(true)

-- Ragdoll and spectate are declared the same way
exports['FeloxAC']:canRagdoll(false)
exports['FeloxAC']:setSpectatorMode(true)
Weapons & damage (client)
None of these give, remove or modify anything by themselves — they whitelist what your own script is about to do. Call the export, then the native.
Whitelist a weapon grant for ~30 s, then hand out the weapon yourself with GiveWeaponToPed. callsite is a free-form label that shows up in the logs (your shop / job name). Blacklisted weapons are refused.
exports['FeloxAC']:removeWeapon(weaponHash)
Drop that whitelist entry when you take the weapon back — otherwise the possession sweep keeps reporting it for 10-25 s.
kind is one of these strings (case-insensitive): weaponDamage, meleeDamage, vehicleDamage, weaponDefense, weaponDefense2, meleeDefense.
local weapon = GetHashKey('weapon_pistol')

-- give a weapon
exports['FeloxAC']:giveWeapon(weapon, 'my-weapon-shop')
GiveWeaponToPed(PlayerPedId(), weapon, 250, false, true)

-- take it back
exports['FeloxAC']:removeWeapon(weapon)
RemoveWeaponFromPed(PlayerPedId(), weapon)

-- per-weapon damage multiplier
exports['FeloxAC']:setDamageModifier(weapon, 1.5)
SetWeaponDamageModifier(weapon, 1.5)

-- ...and when the buff ends
exports['FeloxAC']:removeDamageModifier(weapon)
SetWeaponDamageModifier(weapon, 1.0)

-- player-wide melee buff (gym, PD, safezone...)
exports['FeloxAC']:setPlayerDamageModifier('meleeDamage', 1.8)
SetPlayerMeleeWeaponDamageModifier(PlayerId(), 1.8)

exports['FeloxAC']:removePlayerDamageModifier('meleeDamage')
SetPlayerMeleeWeaponDamageModifier(PlayerId(), 1.0)

-- Drop every weapon whitelist entry at once
exports['FeloxAC']:removeAllWeapons()
RemoveAllPedWeapons(PlayerPedId(), true)

-- Admin tool playing a scenario / animation
exports['FeloxAC']:markToolScenario('WORLD_HUMAN_WELDING', 'my-admin-menu')

-- setNewDamage is the legacy name for setDamageModifier -- identical behaviour
exports['FeloxAC']:setNewDamage(weapon, 1.5)
SetWeaponDamageModifier(weapon, 1.5)
The bridge FeloxAC injects into your resources already calls setDamageModifier on SetWeaponDamageModifier, and removeWeapon / removeAllWeapons on RemoveWeaponFromPed / RemoveAllPedWeapons. GiveWeaponToPed is only auto-reported for resources listed under Safe Scripts — everywhere else you call giveWeapon yourself. The SetPlayer*DamageModifier family is never auto-reported, so setPlayerDamageModifier is always manual.
Open a 5 s input-disable window for admin tools. Keep calling it while the tool stays open.
exports['FeloxAC']:screenshot(webhookUrl)
Capture the local player's screen and upload it. webhookUrl must be a Discord webhook string.
exports['FeloxAC']:captureLastSeconds(webhookUrl)
Upload the local player's last ~10 s of gameplay to that webhook.
exports['FeloxAC']:CreateVehicle(GetHashKey('adder'))
local veh = CreateVehicle(GetHashKey('adder'), x, y, z, heading, true, false)

exports['FeloxAC']:ChangeVehiclePlate(veh, 'FELOX01')
SetVehicleNumberPlateText(veh, 'FELOX01')

-- Peds and objects are declared exactly like vehicles
exports['FeloxAC']:CreatePed(GetHashKey('a_m_y_business_01'))
local ped = CreatePed(4, GetHashKey('a_m_y_business_01'), x, y, z, heading, true, false)

exports['FeloxAC']:CreateObject(GetHashKey('prop_barrier_work05'))
local obj = CreateObject(GetHashKey('prop_barrier_work05'), x, y, z, true, true, false)

-- Whitelist a texture dictionary by name
exports['FeloxAC']:allowTexture('mpleaderboard')

-- Legitimate freecam / admin camera
local cam = CreateCam('DEFAULT_SCRIPTED_CAMERA', true)
exports['FeloxAC']:createCam(cam)
-- ...when you are done
exports['FeloxAC']:destroyCam(cam)
DestroyCam(cam, false)
exports['FeloxAC']:destroyCams()   -- or drop every handle at once

-- Admin tool holding input: keep calling it while the tool stays open
exports['FeloxAC']:disableCamControls()
exports['FeloxAC']:disableAllControls()
Vehicle modifiers (client)
Call these when your script legitimately changes vehicle physics, so the speed-hack layer adopts the new values as its baseline instead of flagging them.
Call
What it does
exports['FeloxAC']:newTopSpeedModifier(value)
Declare a legitimate top-speed multiplier. Values at or below 1.1 are treated as 1.1.
exports['FeloxAC']:newCheatPowerIncrease(value)
Declare a legitimate engine-power increase (nitro, tuning). Same 1.1 floor.
exports['FeloxAC']:newGravity(value)
Declare a legitimate gravity change. Values below 25.0 are treated as 25.0.
exports['FeloxAC']:registerLegalSpeedModifier()
Adopt whatever modifiers are currently applied as legitimate. Call it right after your script finishes applying them.
SetVehicleCheatPowerIncrease(veh, 1.6)
exports['FeloxAC']:newCheatPowerIncrease(1.6)
exports['FeloxAC']:registerLegalSpeedModifier()

-- Top speed and gravity are declared the same way
SetVehicleMaxSpeed(veh, GetVehicleModelMaxSpeed(GetEntityModel(veh)) * 1.4)
exports['FeloxAC']:newTopSpeedModifier(1.4)   -- values <= 1.1 are treated as 1.1

SetGravityLevel(2)
exports['FeloxAC']:newGravity(30.0)           -- values < 25.0 are treated as 25.0
exports['FeloxAC']:registerLegalSpeedModifier()
Ban the local player from a client script. details is an optional table, duration is in seconds and -1 means permanent. Returns whether the ban payload reached the server pipeline.
Confirm FeloxAC's client loop is alive, with its last heartbeat timestamps.
local alive, lastHeartbeat, lastLoopTime = exports['FeloxAC']:isRunning()
if not alive then print('FeloxAC is not running') end

exports['FeloxAC']:banPlayer('Custom client detection', { by = 'my-resource' }, -1)

-- Kick the local player instead
exports['FeloxAC']:kickPlayer('Custom client detection', { by = 'my-resource' })

-- Check an event name before you trigger it
if exports['FeloxAC']:IsEventProtected('myresource:giveMoney') then
    print('this event is protected by FeloxAC')
end
Prefer the Safe Scripts / Safe Events config allowlists when a whole resource or event is legitimate. Use these markers for one-off, per-action allowances inside your own code.
FeloxAC also registers internal exports used by the include/bridge layer it injects into your resources. They are implementation details, they change between builds, and they are not part of this API — do not call them directly.
Ban Export
Use the banPlayer export to ban a player from any server-side script — your admin menu, a custom detection, a report system, and so on. The ban is applied through the same pipeline FeloxAC uses internally, so it is recorded in your ban list, synced to the dashboard, and logged to Discord.
The ban reason (shown in logs and the ban record).
details
table
optional
Extra context logged with the ban (e.g. { by = 'Admin' }).
duration
number
optional
Ban length in seconds. -1 = permanent. If omitted, the configured BanDuration is used.
Returns: a boolean indicating whether the punishment was applied.
duration is measured in seconds, not milliseconds. Use -1 for a permanent ban and a positive number of seconds for a temporary one. Omit it to fall back to your dashboard BanDuration setting.
Examples
Permanent ban
-- Omitting duration uses your configured BanDuration (default: permanent)
exports['FeloxAC']:banPlayer(source, 'Cheating')

-- Or be explicit
exports['FeloxAC']:banPlayer(source, 'Cheating', nil, -1)
Temporary ban
-- Ban for 1 day (86400 seconds)
exports['FeloxAC']:banPlayer(source, 'Toxic behaviour', { by = 'Moderator' }, 86400)
RegisterCommand('myban', function(src, args)
    local target = tonumber(args[1])
    local reason = table.concat(args, ' ', 2)
    if not target or reason == '' then
        return print('Usage: myban [id] [reason]')
    end
    exports['FeloxAC']:banPlayer(target, reason, { by = GetPlayerName(src) }, -1)
end, true) -- restricted command
Ban from another resource via an event
-- In your other resource (server side)
RegisterNetEvent('myac:ban', function(targetId, reason, seconds)
    exports['FeloxAC']:banPlayer(targetId, reason, { by = 'myac' }, seconds or -1)
end)
Always validate who is allowed to trigger a ban. Register admin/ban commands as restricted and never trust a raw client event without permission checks — otherwise a cheater could weaponise your ban handler.
Related exports
Export
Purpose
kickPlayer(source, reason, details?, duration?)
Kick instead of ban.
unbanPlayer(banId, reason, from)
Reverse a ban by its ban ID.
getBanInfo(banId)
Look up a ban record.
unbanAllPlayers(from)
Clear all bans.
Usage Examples
Copy-paste patterns for the most common integrations. All exports are called on the FeloxAC resource.
Admin teleport without a false ban
Mark the teleport as legitimate right before you move the player.
Server side:
RegisterCommand('tp', function(src, args)
    local target = tonumber(args[1]) or src
    exports['FeloxAC']:markExternalTeleport(target)
    -- ... perform your teleport (SetEntityCoords on the target's ped) ...
end, true)
Client side (if you teleport locally):
exports['FeloxAC']:markExternalTeleport()
SetEntityCoords(PlayerPedId(), x, y, z, false, false, false, false)
Admin heal / revive without a false ban
-- Client side, before healing/reviving
exports['FeloxAC']:markExternalHeal()
SetEntityHealth(PlayerPedId(), 200)

-- After a revive
exports['FeloxAC']:playerRevived()
If you use a custom revive event, also set Client Revive Event in the dashboard to that event name so revives never trip a detection.
Give a weapon from a trusted script
The cleanest option is to add your resource to the Safe Scripts list in the dashboard, so its weapon gives are always trusted (see Configuration).
For a per-action allowance from client code instead:
-- Server side: deny a sensitive action to high-threat players
local score = exports['FeloxAC']:getThreatScore(source) or 0
if score > 75 then
    TriggerClientEvent('chat:addMessage', source, { args = { 'System', 'Action temporarily unavailable.' } })
    return
end
Collect evidence on demand
-- Server side: screenshot a suspicious player and post it to Discord
exports['FeloxAC']:screenshot(source, 'https://discord.com/api/webhooks/...')

-- Grab the last ~10 seconds of their gameplay
exports['FeloxAC']:captureLastSeconds(source, 'https://discord.com/api/webhooks/...')
Fix false bans from a job / rental script
If a specific event from a script teleports players or gives them items and causes false bans, add just that event to the Safe Events list in the dashboard (type the event name, press Enter). If the whole resource is trusted, use Safe Scripts instead.
For false bans caused by a spawned object, vehicle, or ped (not by a script), see False Bans.
Spawn entities that the anti-cheat trusts
-- Client side
local veh = exports['FeloxAC']:CreateVehicle(GetHashKey('adder'))

-- Server side
local ent = exports['FeloxAC']:CreateEntity(GetHashKey('prop_barrier_work05'))